What does Roblox game security require?#
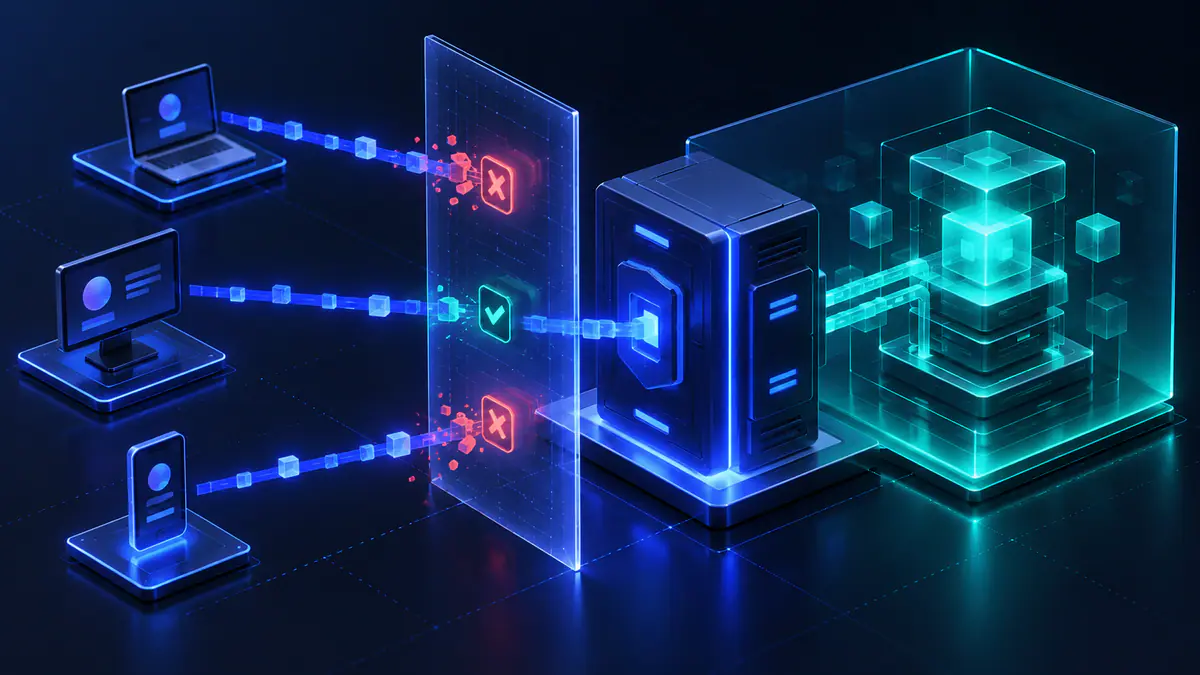
Roblox game security requires a trust boundary between a player’s device and the server’s decisions. The useful question for every feature is: what can the client request, and what must the server independently establish before granting the result?
Roblox’s security tactics make server authority the foundation. A client may present a shop, animate an attack or predict a response, but consequential changes need server authorization. A hidden button is an interface choice, not an access-control rule.
The learning order in this lesson follows that boundary:
- Separate requested actions from authoritative outcomes.
- Define the contract for every client-triggered action.
- Relate exploit behaviors to missing server checks.
- Separate replicated presentation from confidential state.
- Record rejection reasons and verify legitimate gameplay.
The examples below are designs you can review in your own game, not results from a deployed experience. Feature names describe general exploit behaviors, not verified capabilities of a particular script. At redzhub.dev, we fetch loaders as text and never run them, so a status is not proof a script works. For the networking basics, start with RemoteEvents and RemoteFunctions.
Start by deciding which gameplay outcomes only the server may approve.
Server authority and the limits of filtering enabled#
Server authority means the server owns the rules for rewards, inventory, damage and progression. A client can ask to buy an item. The server looks up the price, checks eligibility and decides whether to complete the purchase.
Roblox lists Workspace.FilteringEnabled as deprecated. Treat advice to enable that property as historical guidance rather than a step in securing a current game. Filtering concerns replication; permission checks concern whether server code should perform an action. Those are different responsibilities.
A remote handler can introduce a vulnerability even when arbitrary local edits do not become shared state. If a handler accepts an amount and adds that amount to currency, the handler itself has converted untrusted input into authority. Filtering does not decide whether that grant follows the game’s economy.
Write down who controls each piece of game state. Currency balances, inventory ownership, quest completion and cooldown readiness belong to authoritative server logic. Button visibility, local animation and camera presentation belong to the client. Client displays can reflect server state without becoming the evidence used to authorize changes.
Server decisions do not require server simulation of every object. Roblox distributes physics computation through network ownership. Client-owned assemblies still need checks. Giving the server every moving object can also make gameplay less responsive.
To protect a Roblox game from exploiters, list the state changes you need to protect: spending currency, receiving an item, dealing damage and completing a quest. For each one, write a request contract: what the client may ask for and what the server must check.
How do you secure remote events and their arguments?#
Secure remote events by treating every client argument as an untrusted request and checking it before changing rewards, inventory or other shared state. The same principle applies to RemoteFunctions and other client-triggered interactions; the communication mechanism does not grant permission.
Roblox’s client-server boundary guidance covers context, structure, values and rate limiting. Apply those categories to the purpose of each handler. A cosmetic notification and an inventory transaction need different contracts because their consequences differ.
Argument shape, finite values and bounded work#
A remote handler needs a clear list of accepted fields, types and sizes. Reject an unexpected table where an Instance is required, cap strings and collections before expensive processing, and avoid traversing arbitrary structures sent by the client as though they were trusted game records.
Numeric type checks alone are insufficient. Roblox identifies NaN and infinity as values requiring rejection; a quantity also needs the allowed range and, for indivisible items, an integer requirement. Perform those checks before arithmetic, indexing or serialization can carry an invalid value into another system.
Write down what each accepted field means. An item identifier selects an entry in the server’s catalog; it does not specify a price. A target identifier proposes a candidate; it does not establish that damage is permitted. Avoid accepting redundant fields that the server can calculate, because every extra claim is something else you must check.
Permissions, ownership and action context#
Permission validation asks whether this caller may perform this action now. For a trade, verify that the caller owns each offered item, that the item is tradable and that the trade remains active. For an interaction, verify relevant character state and the interaction’s prerequisites.
Roblox’s remote communication documentation explains how the server receives the sending player. Use that server-provided caller context; do not authorize a request using a user identifier sent inside the request. The client should not get to choose whose permissions the server checks.
An Instance reference also needs contextual validation. A reference to a real object is not proof that the caller owns it or may manipulate it. Resolve the object against the intended server-managed collection and compare it with the caller’s current permissions before changing it.
Rate limits and transaction boundaries#
Rate limits bound how often a caller can request an action. Set the request budget around how often a player should perform the action and how much server work it costs. There is no single threshold for every action. Reject excess traffic before expensive lookups, simulation or persistence work, while retaining gameplay-specific cooldown checks.
A transaction must also handle overlapping requests. Repeated requests must not consume the same item or grant the same reward twice. Reserve or consume the relevant server state as part of the operation, and make sure another handler cannot approve the same resource between the check and the state change.
For a purchase, rejection should leave both balance and inventory unchanged. Acceptance should debit the server-calculated cost and grant the corresponding item as one logical outcome. Check those outcomes directly. A function named “validate” tells you little unless its checks actually protect the balance and inventory.
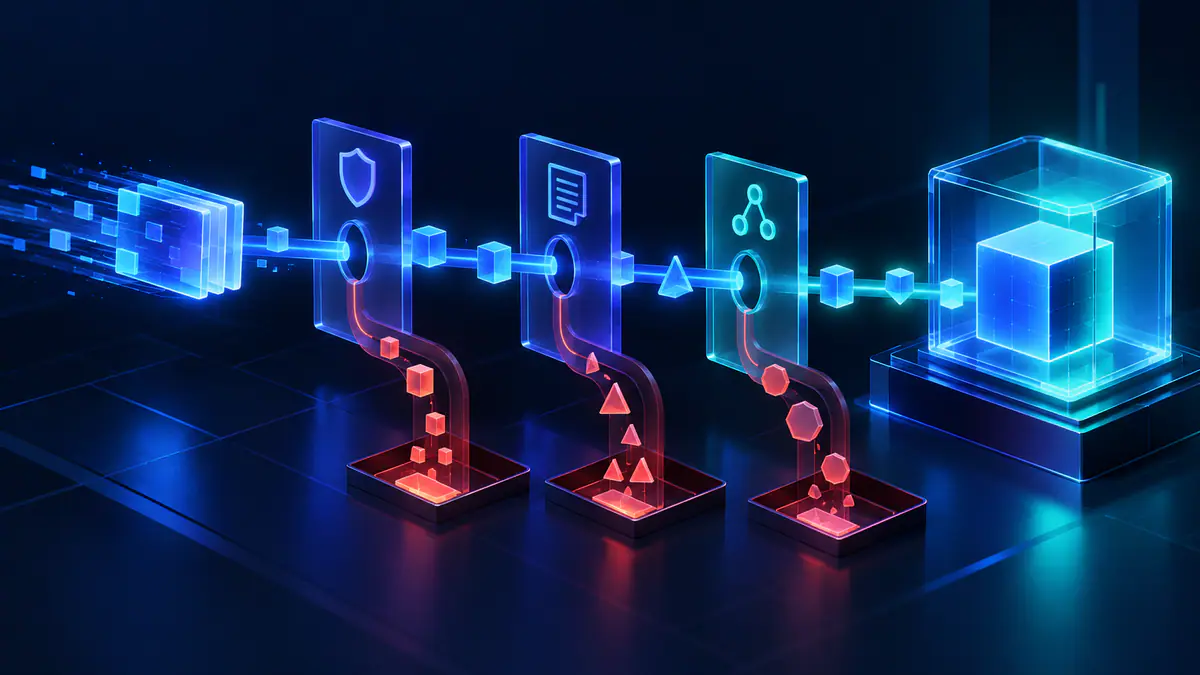
Use each request contract to identify which rule should block an invalid reward or action.
Which server checks address common exploit features?#
Server checks can block invalid rewards, damage and progression; controlling replicated information limits what clients can reveal. Feature labels alone do not identify a vulnerability, so the following table maps generic behaviors to defensive conditions rather than claiming that one rule defeats every implementation.
| Threat category | Untrusted claim or advantage | Server-side defense | Limitation to review |
|---|---|---|---|
| Auto farm | Repeated reward or interaction requests | Validate task state, cooldown, distance and one-time reward consumption | Automation within permitted rules may remain difficult to distinguish |
| Teleport | Presence at a destination without permitted travel | Check movement history and server-authorized transitions before granting objectives | Legitimate portals, respawns and vehicles need context |
| Speed | More movement or actions than rules permit | Compare displacement and action cadence with allowed states | Lag and physics impulses affect observations |
| ESP | Information displayed beyond the intended interface | Avoid replicating confidential information before it is needed | Information already replicated cannot be made secret by hiding UI |
| Kill aura | Damage requested against nearby targets automatically | Validate weapon ownership, attack timing, target rules and reach | Valid attacks can still be automated |
| Spawn items | A request treated as permission to create inventory | Grant items only through server-controlled entitlement or reward paths | Every grant path must enforce the same ownership rules |
Auto farm: authorize progress before granting rewards#
Auto farm checks should establish why a player has earned each reward. For a harvest system, require an eligible resource, a valid interaction state and a harvest opportunity that has not already been used before changing inventory.
A completion message should identify the task being attempted, rather than dictate the reward amount. The server should derive the reward from its own task definition. Replaying the same completion must not create another entitlement after the opportunity has been consumed.
Automation and invalid progression are separate issues. A client can automate requests that satisfy every rule; no argument validator proves that a human pressed a button. Design the economy so permitted actions have permitted outcomes, then evaluate suspicious patterns separately from the reward authorization itself.
Teleport and speed: validate the journey and the interaction#
Teleport and speed threats concern the relationship between position, elapsed time and allowed movement state. A checkpoint system should record eligible transitions and reject a final reward when required earlier stages have not been completed.
Distance alone is a weak entitlement check when the client can influence character movement. A character observed beside a reward may have arrived through an unauthorized transition. Pair proximity with task state and movement context instead of treating a recent position as proof of a legitimate journey.
For a race, distinguish arrival from completion. The server can observe the finish interaction while still withholding a result until the run’s prerequisites are satisfied. That separation keeps reward logic independent from whatever animation or local interface accompanied arrival.
Kill aura and item spawning: verify capability before effect#
Kill aura is a generic label for automated attack behavior; the defensive task is to verify each permitted effect. A melee system should establish that the player has the weapon equipped, can attack in the current state, has respected its cadence and can legitimately affect the target.
The client should not choose authoritative damage, hit count or the contents of another player’s inventory. Resolve combat effects from the server’s weapon and target rules. Account for friendly-fire settings, target validity and range rather than accepting a target reference as an instruction to reduce health.
Item creation needs the same discipline. A player may request an item through a supported gameplay path, but the server must establish the entitlement and choose the template and quantity. A development-only grant interface also needs authorization; removing its visible button does not remove a reachable server handler.
ESP requires a different kind of boundary because the issue is disclosure rather than a requested state change.
Can server checks prevent ESP and exposed secrets?#
Server checks can limit confidential information delivered to clients, but cannot make information secret after delivering it. ESP describes presenting information beyond the intended interface; hiding a nameplate does not remove an underlying replicated object or attribute.
Roblox’s access-control documentation explains that replicated content can be inspected even when it is not visible or used. Treat the replicated data model as readable by the receiving player. Review hidden objectives, unrevealed roles and other confidential state before adding them to shared objects.
Consider a hidden-role game. The server can keep the role assignment private and send each player only information needed for that player’s interface. Placing everyone’s role in replicated attributes and concealing the display leaves the information boundary open, regardless of how the interface is drawn.
Asset streaming and visual occlusion should not be treated as universal confidentiality guarantees. Ask which information a recipient actually receives, including remote responses and later updates. An authorization check on a data-returning request matters as much as a check on a request that changes inventory.
Credentials need an even stricter rule: never store secrets client-side. Avoid embedding external service credentials, administration passwords or privileged tokens in replicated code, configuration or responses. Server-side permission checks should decide access without expecting the client to keep a shared password private.
Check module and data placement next: location determines what reaches clients.
ModuleScript placement and replicated data#
ModuleScript placement controls who can receive the module, while the caller determines the execution context. A module intended for server use is still exposed if clients receive it.
Roblox’s data model documentation distinguishes replicated containers from server-only containers. Use that distinction to separate presentation utilities from authoritative implementation. Shared constants may be appropriate for replication; private entitlement logic and confidential state need a server-only location.
| Location | Intended role in this lesson | Security review question |
|---|---|---|
| ServerScriptService | Server execution and server-only modules | Does the entry script authorize every external request? |
| ServerStorage | Server-only assets and modules required by server code | Does an asset remain private until intentionally replicated? |
| ReplicatedStorage | Shared modules, remote objects and client-needed assets | Would disclosure of every descendant violate the design? |
| Client script containers | Input, presentation and local feedback | Does any consequential rule depend solely on client enforcement? |
A ModuleScript in ReplicatedStorage is exposed even if no LocalScript requires it. A conditional branch intended for the server does not make the rest of a replicated module confidential. Split shared definitions from private implementation rather than placing both in one module and relying on execution conditions.
ServerStorage is also not a substitute for a running server entry script. Organize modules there when server code will require them, and keep the scripts that start server behavior in an appropriate execution container. The placement review should cover cloned assets too: an object becomes a disclosure concern when the server moves or copies it into a replicated location.
A server-only implementation still needs movement-aware checks when its decisions depend on client-influenced physics.
How should movement sanity checks handle legitimate travel?#
Movement sanity checks should compare observations against the movement rules active for that character, including server-authorized exceptions. A single displacement threshold cannot describe walking, vehicle travel, knockback, spawning and portals equally well.
Roblox’s movement and physics security guidance explains why client-owned physics cannot be treated as trustworthy evidence by itself. Use movement observations to constrain interactions and investigate anomalies, rather than assuming a property read establishes the player’s complete travel history.
A movement record can track the last accepted position, observation time, movement mode and authorized transition. Base the allowed movement range on the game’s actual rules. Reject invalid numeric components before distance calculations, and avoid treating an absent character during respawn as an ordinary movement sample.
Server-authorized teleports need explicit context. Record the destination or transition when the server permits travel, then reset the movement baseline as part of that operation. Do not grant an unrestricted exception because the client reports that a teleport occurred.
Latency, moving platforms and impulses complicate interpretation. Review those cases in controlled gameplay before imposing consequences. A movement anomaly may justify withholding an objective reward or restoring a last accepted position without proving deliberate misconduct.
Compare “configured speed” with “observed travel” when reviewing a movement check. Restoring a configured movement property does not establish that a player stayed within a permitted route. Objective authorization should still depend on the states that make the objective valid.
Rejection logs help you distinguish an invalid request from a broader pattern of abuse.
Honeypot remotes, logging and proportionate responses#
Honeypot remotes are decoy endpoints that legitimate clients are not meant to call. Roblox describes them in server-side detection and consequencing, alongside behavioral heuristics and proportionate responses. Their role is supplementary detection, not authorization for real gameplay actions.
Before adding a decoy, verify that legitimate code, old clients and development tools cannot call it accidentally. Document its purpose and review logs before attaching consequences. A deployment mistake that introduces legitimate traffic changes the interpretation of the signal, even when the endpoint was designed to receive none.
For ordinary handlers, log the server time, caller identifier, action, rejection category and relevant authoritative context. Record categories such as invalid type, missing entitlement, consumed reward or exceeded budget. Avoid storing credentials or entire unbounded payloads merely to explain a rejection.
Aggregate repeated events so that logging cannot become another expensive operation triggered by traffic. Keep enough context to tell whether one bug keeps repeating or several different checks are failing. A counter without the handler and rule context is difficult to use when a new release changes legitimate behavior.
Behavioral analysis should support investigation. Consistent timing or rapid resource gain can have alternative explanations, including intended automation or a gameplay defect. Prevent invalid state changes first; escalate consequences according to the strength of the evidence and the potential harm.
Write down which rule rejects a request, which system logs it and who reviews possible consequences. Give each responsibility an owner so a release does not leave rejected requests unreviewed or punishments unexplained.
Practice: review a reward claim before release#
A reward remote should grant a quest reward only when the server can establish completion. For this exercise, design a request that accepts a task identifier. Check whether the server can approve it without trusting a reward amount, progress counter or completion timestamp reported by the client.
- Write the accepted request. Permit only fields needed to identify the intended action. Checkpoint: every field has a purpose and bound. Common mistake: accepting a reward amount simply because the interface already displays it.
- Resolve server state. Find the player’s active task and reward definition. Checkpoint: the task belongs to the caller and is eligible. Common mistake: looking up a valid task without checking that this player has it.
- Authorize completion. Establish the required progress and travel context. Checkpoint: all prerequisites exist in authoritative state. Common mistake: treating a finish interaction as proof of every earlier stage.
- Consume and grant. Prevent overlapping requests from granting the same entitlement twice. Checkpoint: rejection changes nothing, and acceptance consumes one completion opportunity. Common mistake: granting first and marking completion later.
- Inspect failure cases. Include missing identifiers, wrong types, repeated claims and requests during a state transition. Checkpoint: rejection is bounded and explainable. Common mistake: checking only the path used by the current interface.
The answer: the client selects a task, and the server decides whether it is complete. A valid-looking identifier is necessary but insufficient: ownership, prerequisites, timing and consumption state determine whether the reward may be granted.
Roblox’s Studio testing modes provide client and server simulations for examining a developer’s own experience. Verify expected play alongside invalid requests, including concurrent clients and character transitions. These examples have not been run in Studio, and we report no measured detection rate.
For Luau syntax preparation, use getting started with Luau; for the broader learning sequence, return to the Roblox development lessons. Record the missing checks before you release the feature.
A practical Roblox game security review#
A Roblox game security review should list every route that changes rewards, items, damage or progression, the server conditions it must satisfy and how you will check rejection. Prioritize currency, inventory, combat and progression before supplementary detection, then review movement assumptions and replicated information.
Finish the review when each entry point has a written request contract, a clear owner for the authoritative state and controlled checks for accepted and rejected requests. No generic checklist establishes that an entire experience resists every exploit. Adapt these examples to your game’s rules and architecture, then check them against legitimate play. A rule that rejects a valid portal trip needs attention just as a rule that grants the same quest reward twice does.
Third-party code brings a separate risk: we fetch loaders as text and never run them, so a listing status does not prove a script works. Using third-party scripts or executors breaks Roblox’s Terms of Use, and accounts can be banned. The redzhub.dev methodology explains the index’s evidence labels; those labels do not establish that a developer’s server is secure. Continue the security review whenever a feature introduces a new reward path, client-triggered interaction or disclosure of previously private state.